
Cybersecurity headlines are data-layer warnings.
Threat analysis, breach lessons, and Cyberstorage guidance for organizations defending unstructured data.
Latest
All threat briefs →Threat Brief
The DHS employee data leak: 41,000 records out, and “what happened?” is still the open question
October 29, 2026 • 6 min
Threat Brief
AI agents reached Anthropic’s business systems through third-party SaaS in under 12 hours
October 27, 2026 • 5 min
RackTop Perspective
Your AI Agent Has an Activity Log. But Who’s Auditing the Data?
October 20, 2026 • 8 min
Federal & Defense
Labels you can enforce: a manager’s guide to metadata hygiene for Zero Trust, ACP 240, and STANAG
October 19, 2026 • 7 min
New here? Start with these
Three pieces that explain the category, the mechanism, and the limit of the tools most organizations already own.
- 1
What Cyberstorage is, and why it exists
Cyberstorage builds security and recovery into the data storage layer itself. Here is what that means, the thirty-year assumption that made the category necessary, why Gartner named it in 2021, and how it differs from backup and traditional NAS.
7 min read
- 2
Ransomware protection at the storage layer: how it actually works
What real ransomware protection looks like at the layer attacks actually touch: the visibility, detection, policy, response, recovery, and evidence chain, explained link by link.
9 min read
- 3
Backup is necessary. It is not a security control.
Immutable backups matter. But a recovery copy cannot see an attack, cannot stop exfiltration, and cannot tell you that data was stolen. Treating backup as security leaves the live data undefended.
5 min read
Cyberstorage Explainers
Plain-language explanations of the architecture and the category.

How long do data breaches go undetected? What dwell time measures, and what it leaves out
Mandiant puts the median dwell time at 14 days. IBM puts the average time to identify a breach at 183. Both are right, and neither says how long it takes to learn what an attacker took.
October 2, 2026

What Cyberstorage is, and why it exists
Cyberstorage builds security and recovery into the data storage layer itself. Here is what that means, the thirty-year assumption that made the category necessary, why Gartner named it in 2021, and how it differs from backup and traditional NAS.
July 12, 2026
Ransomware protection at the storage layer: how it actually works
What real ransomware protection looks like at the layer attacks actually touch: the visibility, detection, policy, response, recovery, and evidence chain, explained link by link.
July 12, 2026
Practitioner Guides
Hands-on guidance for storage, security, and SOC teams.
Body-worn camera storage: retention, chain of custody, and CJIS
Body-worn camera video is the largest and fastest-growing data set most departments own. Here is how to store it for years, prove who touched each file, keep it inside CJIS controls, and get it back after a ransomware attack.
October 14, 2026
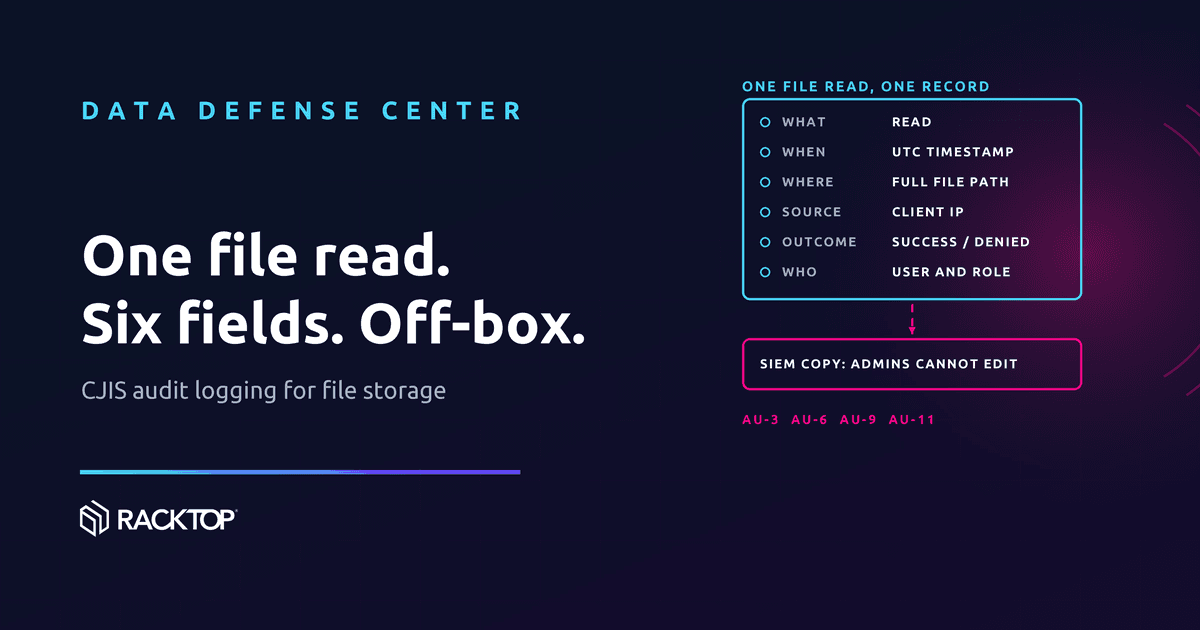
CJIS audit logging requirements for file storage
The CJIS audit controls read directly against the storage holding CJI. Here is what each one asks for, what an auditor will want to see, and where file shares usually fall short.
October 14, 2026
CJIS storage checklist: 15 questions for any vendor holding your CJI
No storage product is CJIS certified, so a vendor’s CJIS page tells you little. These fifteen questions turn the CJIS v6.1 controls into answers you can check, and we answer every one of them for BrickStor SP.
October 14, 2026
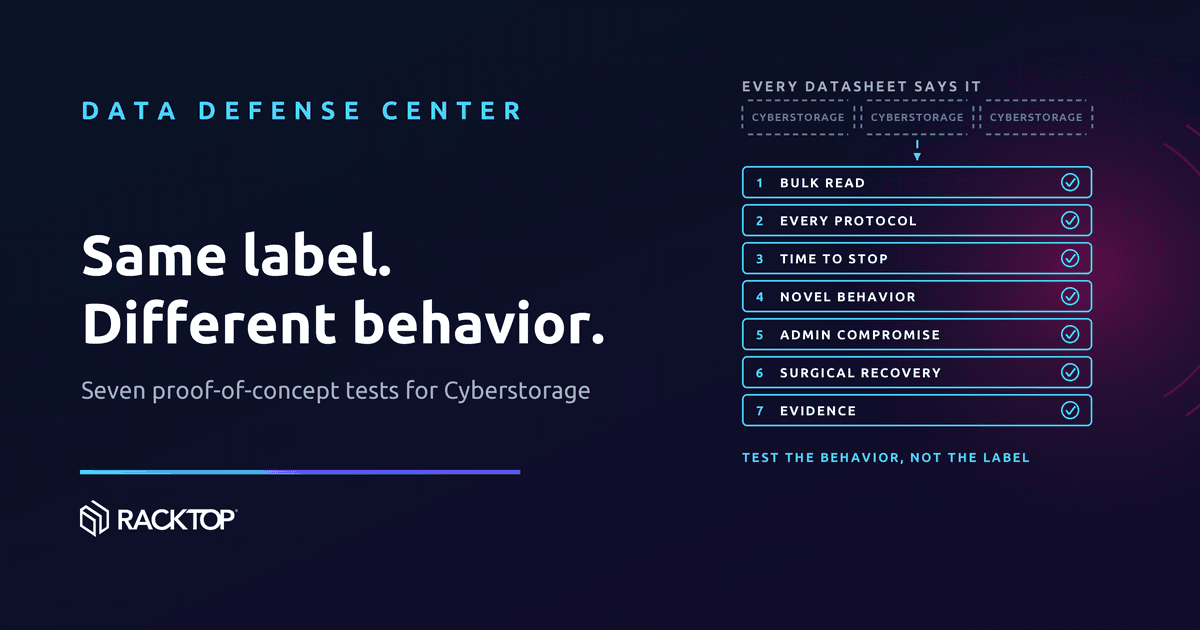
When every storage product claims Cyberstorage: seven tests that tell them apart
Gartner expects every storage product to include Cyberstorage capabilities by 2029. When the label is universal, a datasheet stops telling buyers anything. Seven live tests for a proof of concept still can.
September 23, 2026
Executive Briefings
Board-level framing of unstructured-data risk and resilience.

Recovery time is now a disclosure question
Regulators, insurers, and customers increasingly ask the same two questions after an incident: how fast were you back, and what exactly was taken? Both answers are determined at the data layer, before the incident ever happens.
June 30, 2026
A board-level view of unstructured data risk
Most of an organization’s data is unstructured files, and most of its risk concentrates there. A short briefing for executives on why the storage layer belongs on the risk register.
May 28, 2026
Federal & Defense Notes
Zero Trust, classification, and mission-data guidance for government.
Labels you can enforce: a manager’s guide to metadata hygiene for Zero Trust, ACP 240, and STANAG
Zero Trust and coalition data sharing both depend on one thing most programs underfund: accurate labels on files. What the standards expect, where labels usually go wrong, and the questions a program manager should be asking.
October 19, 2026
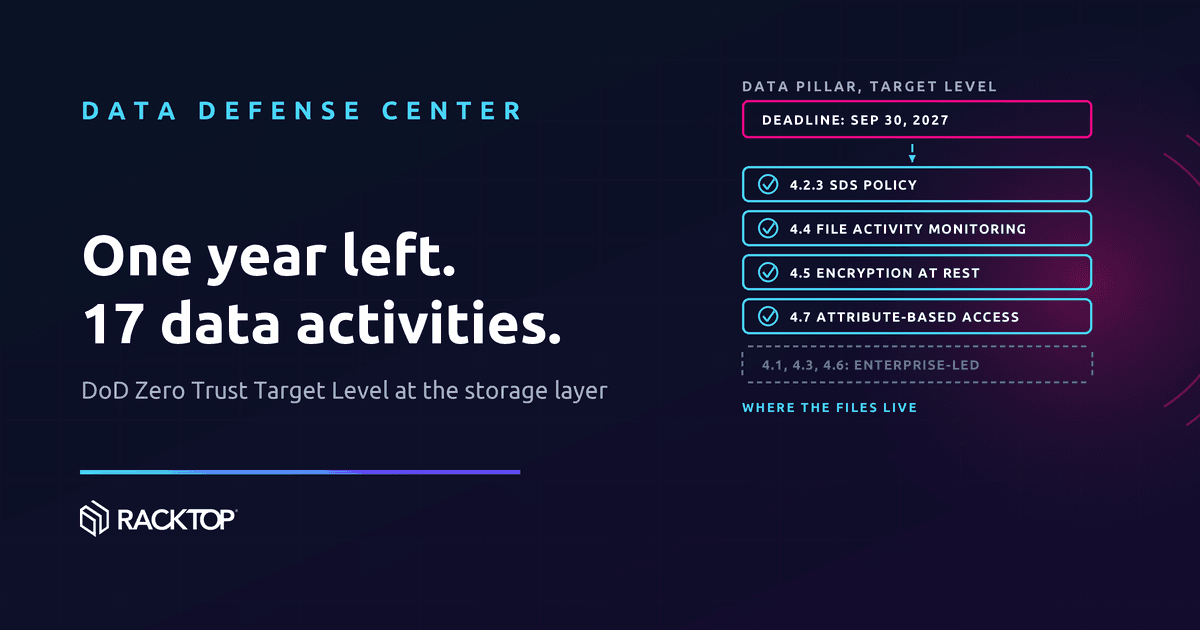
FY2027 is here: what the DoD Zero Trust data pillar requires, and what storage has to prove
Fiscal 2027 began October 1, the last year components have to reach Target Level Zero Trust. Seventeen of the 91 Target activities sit in the data pillar, and several of them land on storage.
October 5, 2026
CJIS Security Changes for 2026 and 2027: What State and Local Agencies Need to Know
Two dates shape CJIS planning for state and local agencies: the FIPS 140-2 sunset, which took effect on September 22, 2026, and the end of the zero-cycle period on September 30, 2027. Here is what each one actually requires, and why so much of the work lands on storage.
August 21, 2026
Harvest now, decrypt later: post-quantum encryption reaches the data layer
Two executive orders, three NIST standards, and NSA’s CNSA 2.0 have turned post-quantum cryptography from research topic into procurement requirement. What the mandates actually say, and how BrickStor SP is post-quantum ready for data at rest and data in transit.
July 27, 2026
Healthcare, Critical Infrastructure & Enterprise IT
Sector-specific data-defense pressures and lessons.
Government data breaches in 2026: a running list, and the patterns underneath it
A running list of notable 2026 government data breaches, from county networks to the FBI and the Pentagon, updated monthly, with the patterns that repeat across them.
October 1, 2026

Why healthcare keeps paying the highest breach costs
Healthcare has carried the highest average breach cost of any industry for more than a decade. The five reasons why trace back to the data itself: sensitive, regulated, sprawling, and largely unstructured.
July 12, 2026
Critical infrastructure’s quiet exposure: the IT file share
Utilities invest heavily in OT security while the IT side (engineering diagrams, SCADA documentation, customer data on ordinary file servers) remains the softer target attackers actually take.
July 12, 2026
RackTop Perspective
Points of view from the team that pioneered Cyberstorage.
Your AI Agent Has an Activity Log. But Who’s Auditing the Data?
Microsoft is giving AI agents identities and expanding monitoring. But knowing which agent acted is not the same as independently verifying which files were accessed or changed.
October 20, 2026
The archive keeps the risk. It loses the controls.
Tiering data to cheaper storage changes what it costs to keep. It does not change what it costs to lose. Archived files keep every property that made them sensitive and usually shed the monitoring, access control, and audit that protected them.
September 8, 2026
Before the ransom note: what hackers learn from your files
Ransomware is the loudest threat to unstructured data, but it is not the first one. Hackers and APTs read your files long before they encrypt anything, and what they learn shapes the entire attack. Cyberstorage exists because protection has to start at the read, not the ransom note.
August 9, 2026

Two exabytes, and no one agrees who owns it: the AI World Cup and the data layer
The 2026 World Cup is projected to generate roughly 90 petabytes of tournament data, and some two exabytes overall. Almost none of it is rows in a database. The harder problem is not storing it: ownership is a bundle of contractual rights, and only the data layer can prove who actually touched what.
July 14, 2026
Latest Threat Briefs
Analysis of active threats and what they mean for data at the storage layer.
The DHS employee data leak: 41,000 records out, and “what happened?” is still the open question
A searchable database of more than 41,000 DHS employees and contractors went public on October 28, 2026, and the department still calls it a potential breach. Once a breach is suspected, the records you already keep decide whether “what happened?” takes hours or weeks.
October 29, 2026
AI agents reached Anthropic’s business systems through third-party SaaS in under 12 hours
A startup’s AI agents failed for days against Anthropic’s own systems, then got in through third-party sales, HR, and IT software in under 12 hours. The two sides disagree about what was reached, and that is the lesson.
October 27, 2026
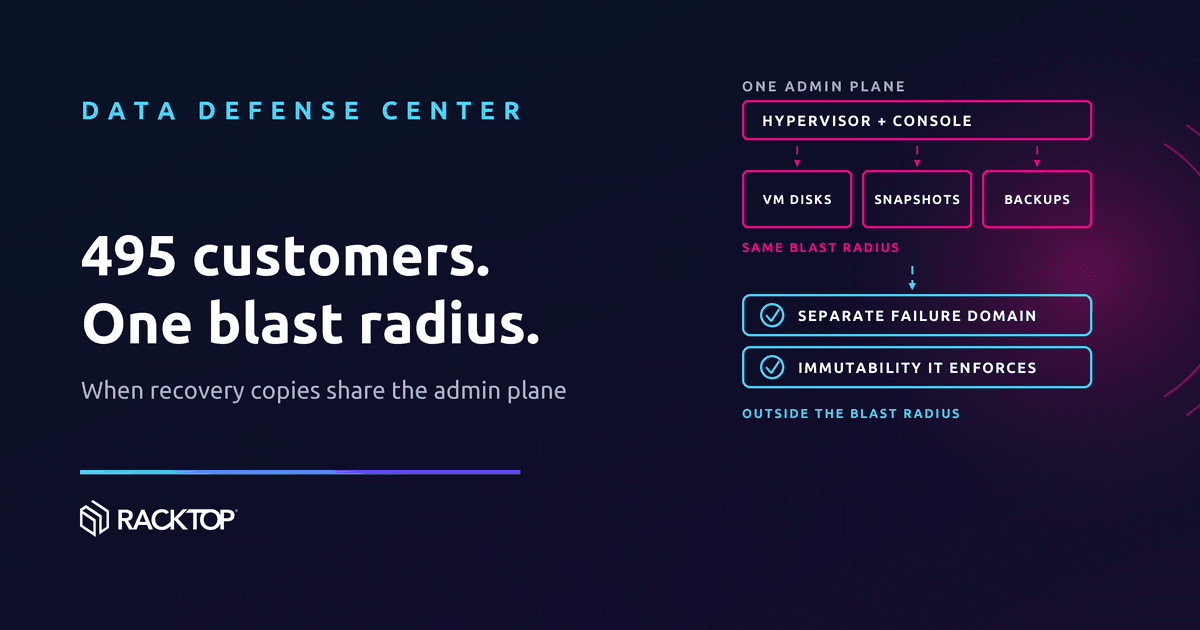
When ransomware takes the snapshots too: the IDCF Cloud attack, and how to keep recovery copies out of reach
Ransomware shut down servers for 495 customers of a Japanese cloud service, and the provider told them to rebuild from their own backups. Here is how RackTop deploys BrickStor SP so the data, and every copy of it, sits outside the attacker’s reach.
October 13, 2026

The FBI jobs portal claim: a recruiting front door, and what the attackers say sat behind it
ShinyHunters defaced FBIjobs.gov and claims it reached HR, medical, and psychiatric evaluation records from there. The FBI has acknowledged employee data was stolen but has not said where the breach began, which is the question a file-level audit answers.
October 2, 2026
Looking for datasheets, validations, and case studies? Visit the Resource Library →
See data-layer defense in your environment
In a 30-minute demo we’ll show Active Defense stopping an attack inline, immutable recovery, and surgical rollback — mapped to your data and your threats.